highData Breaches
ASOS Data Breach Highlights Identity Risks in Customer-Facing SaaS Platforms
Compromised identity used as foothold for lateral movement into corporate network
Cyber.TechVoid1 min read

Key Takeaways
- A data breach at ASOS exposed customer data, with initial access traced to a compromised identity.
- The threat actor leveraged a customer-facing SaaS platform to penetrate the corporate network.
- The incident demonstrates the risk of lateral movement from customer-facing services into internal systems.
- Robust identity and access management, as well as SaaS security hardening, are critical mitigation strategies.
Related Security News
mediumData Breaches
ASOS Confirms Data Breach Following Social Engineering Attack
ASOS has confirmed a cybersecurity incident involving unauthorized access to customer personal data. The breach is linked to a social engineering attack aimed at credential theft, with affected customers receiving notification updates this week.
BleepingComputer1 min read
highData Breaches
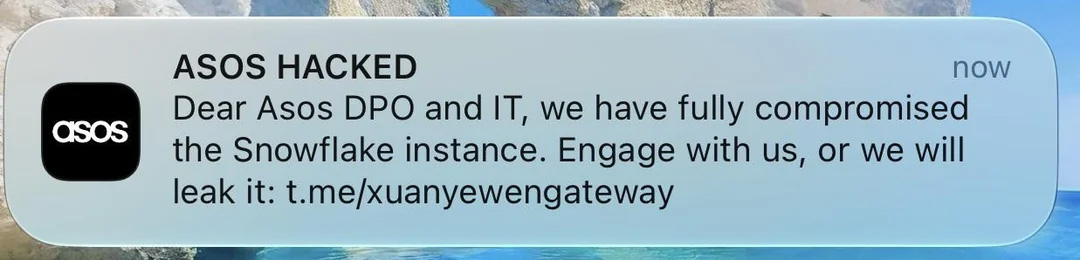
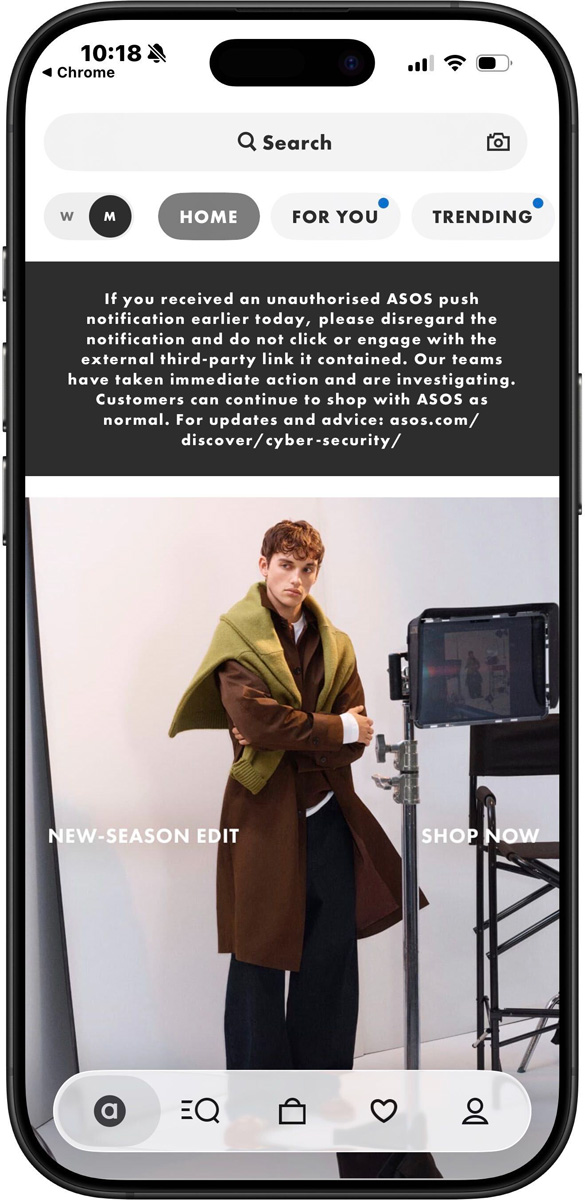
ASOS Confirms Data Breach Following Unauthorized In-App Notifications
ASOS has confirmed a data breach after unauthorized push notifications were sent through its mobile app. The threat actors claim to have stolen customer data from the company's Snowflake environment, though details regarding the scale and specific data elements remain unverified.
BleepingComputer1 min read