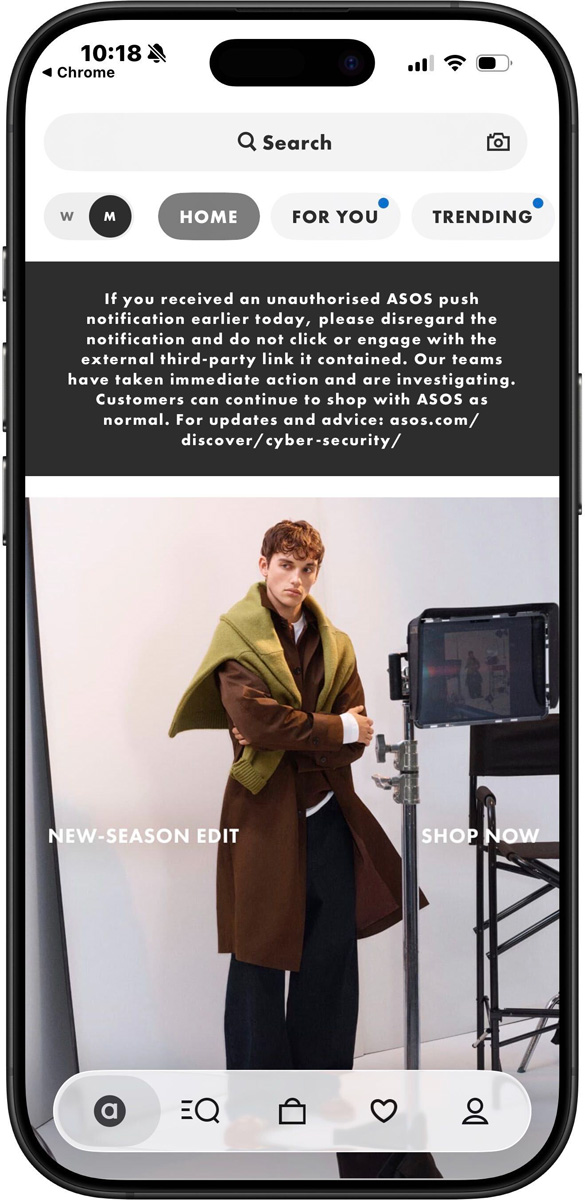
ASOS Confirms Data Breach Following Social Engineering Attack
Hackers accessed customer personal data via credential theft; company notifies affected users
Key Takeaways
- ASOS confirmed a data breach linked to a social engineering attack and credential theft.
- Customer personal data was accessed, and affected users are being notified.
- The exact scope of data compromised and technical details of the attack vector are not publicly specified.
- No software patch is required; mitigation involves credential management and MFA enforcement.
Quick answers
- What happened?
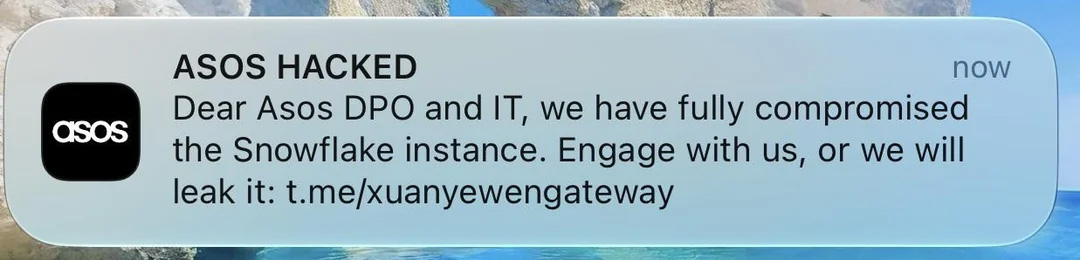
- ASOS has confirmed a cybersecurity incident involving unauthorized access to customer personal data. The breach is linked to a social engineering attack aimed at credential theft, with affected customers receiving notification updates this week.
- What should defenders do?
- Affected customers should reset passwords, enable multi-factor authentication where available, and remain vigilant for phishing attempts. ASOS should enforce credential resets, review access controls, and conduct security awareness training for staff.
Retailer ASOS confirmed on October 8, 2026, that hackers accessed some personal data belonging to customers. The company stated the incident was linked to a social engineering attack involving credential theft. ASOS has begun sending updates to affected customers notifying them of the breach. While the company confirmed that personal data was accessed, specific details regarding the exact categories of data compromised or the full scope of the impact have not been publicly disclosed. The attack vector is reported to involve social engineering techniques, though technical specifics remain pending. No software patch is applicable; mitigation focuses on credential resetting, multi-factor authentication enforcement, and employee training.
Security Details
The breach was initiated through a social engineering attack aimed at obtaining credentials. The specific techniques used (e.g., phishing, pretexting) and the exact data fields accessed have not been disclosed. ASOS has confirmed that personal data was compromised but has not specified whether financial or highly sensitive identifiers were included.
Mitigation
Affected customers should reset passwords, enable multi-factor authentication where available, and remain vigilant for phishing attempts. ASOS should enforce credential resets, review access controls, and conduct security awareness training for staff.
Sources
BleepingComputer
ASOS links data breach to social engineering attack, credential theft
Oct 8, 2026 · 11:42
Original link
Related Security News

ASOS Data Breach Highlights Identity Risks in Customer-Facing SaaS Platforms
A data breach at British online fashion retailer ASOS has exposed customer data, with investigations revealing that a compromised identity served as an initial access point, enabling deeper penetration of the corporate network through a customer-facing SaaS platform. The incident underscores the security risks associated with third-party integrations and the need for robust identity and access management.