ASOS Confirms Data Breach Following Unauthorized In-App Notifications
Hackers claim Snowflake compromise; retailer validates breach impact
Key Takeaways
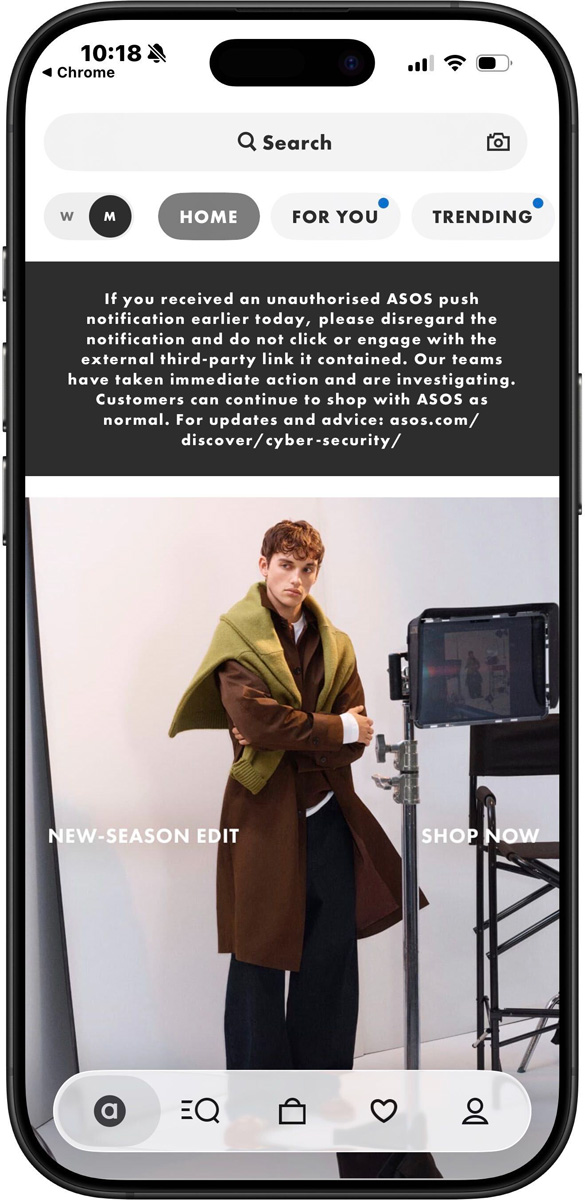
- ASOS confirmed a data breach following unauthorized push notifications sent via its mobile app.
- Threat actors claim to have exfiltrated customer data from ASOS's Snowflake environment.
- Details regarding the scale of the breach, number of affected customers, and specific data elements remain unverified.
- Snowflake environment involvement requires further confirmation and analysis.
- ASOS has not disclosed the technical method used to gain access to the cloud storage system.
Quick answers
- What happened?
- ASOS has confirmed a data breach after unauthorized push notifications were sent through its mobile app. The threat actors claim to have stolen customer data from the company's Snowflake environment, though details regarding the scale and specific data elements remain unverified.
- Which products are affected?
- Snowflake
- What should defenders do?
- ASOS customers are advised to monitor accounts for unusual activity, update passwords if reused, and remain alert for phishing attempts. The company should conduct a full forensic investigation of the Snowflake environment, rotate credentials, and enforce multi-factor access controls. Users should verify any communications claiming to be from ASOS.
UK fashion retailer ASOS confirmed a data breach on Tuesday following reports that hackers sent unauthorized push notifications through its mobile app. The threat actors accompanied the notifications with claims of having stolen customer data from ASOS's Snowflake cloud environment. ASOS validated the breach incident, stating that unauthorized access occurred, but has not disclosed the exact number of affected customers or the specific categories of data compromised. Security researchers note that Snowflake environment intrusions have been observed in recent threat activity, though the full scope of this incident requires further investigation. The company has not provided a detailed technical breakdown of the breach mechanism at this time.
Security Details
Unauthorized push notifications were sent through the ASOS mobile app. Threat actors claim exfiltration of customer data from a Snowflake cloud environment. Exact breach scope, affected data categories, and number of compromised records have not been disclosed by ASOS.
Affected products
Snowflake
Mitigation
ASOS customers are advised to monitor accounts for unusual activity, update passwords if reused, and remain alert for phishing attempts. The company should conduct a full forensic investigation of the Snowflake environment, rotate credentials, and enforce multi-factor access controls. Users should verify any communications claiming to be from ASOS.
Sources
BleepingComputer
ASOS confirms data breach after “HACKED” in-app notifications
Oct 6, 2026 · 16:33
Original link
Related Security News
Denmark Central Population Register Data Breach Exposes 8.8 Million Records
Denmark's Central Population Register (CPR) has confirmed a data breach affecting approximately 8.8 million registered individuals. The exposed data includes sensitive personal information, prompting warnings of increased risks for identity theft, phishing, and social engineering. Official details regarding the root cause and specific data elements remain under investigation.