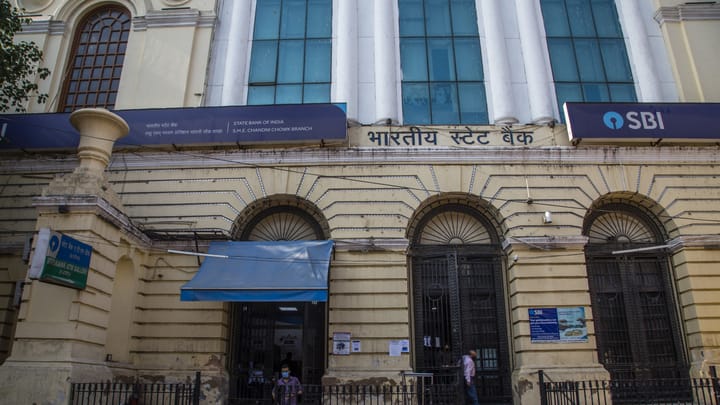
State Bank of India Customer PII Data Leak Reported
Underground Market Activity Amplifies Risk for SBI Customers
Key Takeaways
- State Bank of India confirmed a customer PII data leak.
- The breach is characterized as relatively small but amplified in severity by underground market trading of the data.
- Affected customers are at increased risk of phishing, identity theft, and financial fraud.
- No software patch is applicable; mitigation focuses on data protection and customer vigilance.
Quick answers
- What happened?
- State Bank of India has confirmed a customer PII data leak. While characterized as a relatively small breach, the sophistication of the underground market for trading personally identifiable information has amplified the severity of the incident. Affected customers face increased risks of targeted phishing, identity theft, and financial fraud.
- What should defenders do?
- State Bank of India and affected customers should remain vigilant. Recommended actions include strengthening data protection monitoring, scanning dark web forums for leaked data, and advising customers to be cautious of phishing attempts and fraudulent communications. No software patch is applicable for this incident.
According to a report published by Dark Reading on October 23, 2026, State Bank of India (SBI) is dealing with a customer PII data leak. The source indicates that the breach, while described as relatively small in scale, has taken on heightened seriousness due to the activity of a sophisticated underground market engaged in trading PII. The exact volume of data leaked and the specific categories of personally identifiable information compromised have not been detailed in the available summary. The report notes that the sophistication of the underground market amplifies the risk to customers. Potential impacts include targeted phishing campaigns, identity theft, and financial fraud. As of the report, no software patch is applicable, as the incident involves a data leak rather than a software vulnerability. Mitigation efforts are likely focused on SBI strengthening its data protection controls, monitoring dark web forums for leaked data, and advising customers to remain vigilant against phishing and fraudulent activity.
Security Details
The incident involves a customer PII data leak. The source indicates the breach is relatively small in scale but has become serious due to the involvement of a sophisticated underground market for trading personally identifiable information. Specific technical details regarding the attack vector or the exact data types leaked are not provided in the summary.
Mitigation
State Bank of India and affected customers should remain vigilant. Recommended actions include strengthening data protection monitoring, scanning dark web forums for leaked data, and advising customers to be cautious of phishing attempts and fraudulent communications. No software patch is applicable for this incident.
Sources
Dark reading
State Bank of India Suffers a Customer PII Data Leak
Oct 23, 2026 · 03:30
Original link
Related Security News

Railway Urges Users to Rotate Secrets Following Potential Security Incident
Railway, a cloud development platform, has issued an urgent advisory prompting users to rotate all secrets, API keys, and environment variables. The warning follows the detection of suspicious activity on the platform's systems earlier this week. While no confirmed exploitation or data exfiltration has been reported, the company is treating the incident as a potential breach requiring immediate credential rotation.