SickKids Data Breach Exposes Employee and Job Applicant Information
Third-party software flaw leads to exposure of personal data at Toronto's Hospital for Sick Children
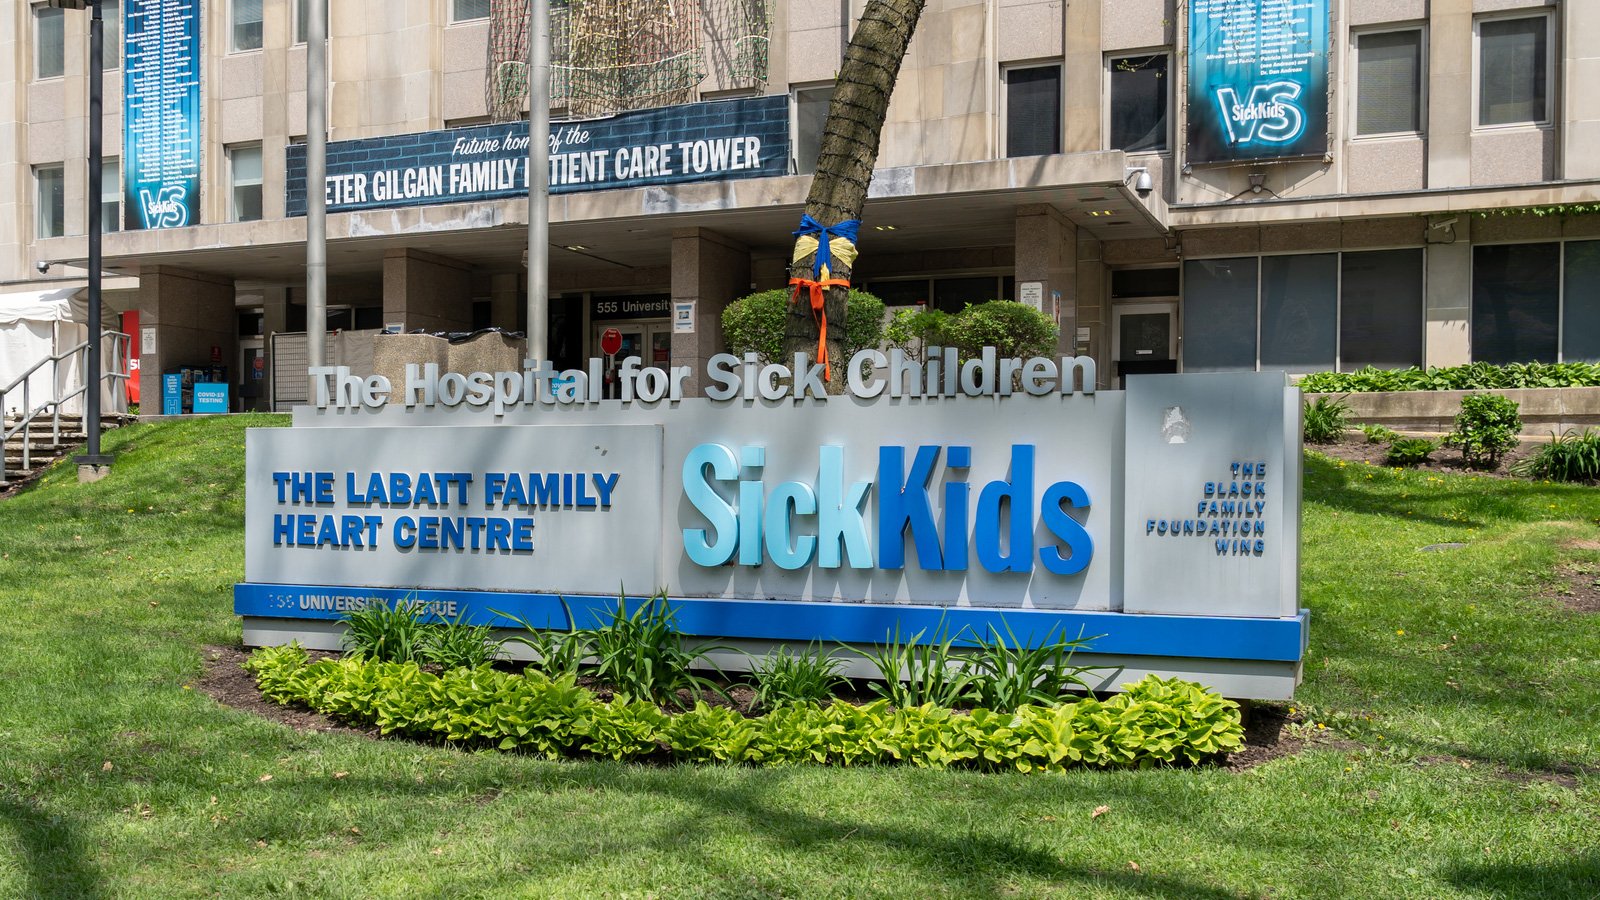
Key Takeaways
- A cybersecurity incident at SickKids exposed personal information of employees and job applicants.
- The breach was caused by a flaw in third-party software.
- Clinical systems and patient records were confirmed unaffected.
- The incident was disclosed on August 21, 2026, with occurrence preceding disclosure.
- Specific technical details, scope of data exposed, and remediation status are pending confirmation.
Quick answers
- What happened?
- Toronto's Hospital for Sick Children (SickKids) confirmed a cybersecurity incident that exposed the personal information of current and former employees and job applicants. The breach stemmed from a flaw in third-party software, and the organization confirmed that clinical systems and patient records remained unaffected.
- What should defenders do?
- SickKids is likely engaged in remediation of the vulnerable third-party software. Affected individuals are advised to monitor accounts for unusual activity. Organizations relying on third-party software should conduct vendor risk assessments and ensure timely patching of integrated components.
Toronto's Hospital for Sick Children (SickKids) has confirmed a cybersecurity incident that exposed the personal information of some current and former employees and job applicants. According to the organization, the breach originated from a flaw in third-party software. SickKids emphasized that clinical systems and patient records were not affected by the incident. The notification was published on August 21, 2026, though the incident occurred prior to disclosure. Details regarding the specific third-party software involved, the exact number of affected individuals, and the current remediation status remain pending confirmation. BleepingComputer reported on the incident, noting that no ransomware demands or active exploitation details have been publicly disclosed at this time.
Security Details
The breach leveraged a flaw in third-party software used by SickKids. No details have been released regarding the nature of the vulnerability, whether it was actively exploited prior to discovery, or if any patches have been applied. SickKids confirmed that clinical systems and patient records were not affected, indicating the incident was confined to HR and applicant-facing systems.
Mitigation
SickKids is likely engaged in remediation of the vulnerable third-party software. Affected individuals are advised to monitor accounts for unusual activity. Organizations relying on third-party software should conduct vendor risk assessments and ensure timely patching of integrated components.
Sources
BleepingComputer
SickKids data breach exposes employee and job applicant info
Aug 21, 2026 · 10:10
Original link
Related Security News

Times Car Confirms Data Breach Affecting 6.6 Million User Accounts
Times Car, a Japanese car-sharing service, has confirmed a data breach compromising approximately 6.6 million user accounts. The incident was disclosed late last week, with the exact attack vector and nature of exposed personal information yet to be fully specified. Authorities and the company are reportedly investigating the breach.

Misconfigured Supabase Apps Expose Data in Over 16,000 Databases
Security researchers have identified more than 16,000 Supabase-backed applications with publicly accessible databases. The exposure stems from default allow rules that permit unrestricted read access to tables containing personally identifiable information, passwords, and authentication tokens. The findings highlight the risk of misconfigured backend-as-a-service platforms when security defaults are not adjusted for production use.