Prophet Security Analysis Reveals Identity as Primary Target in Half of Malicious Activity Across Q2-Q3 2026
Quarterly alert investigation identifies four dominant attack patterns, with identity-focused threats comprising approximately 50% of confirmed malicious activity.
Key Takeaways
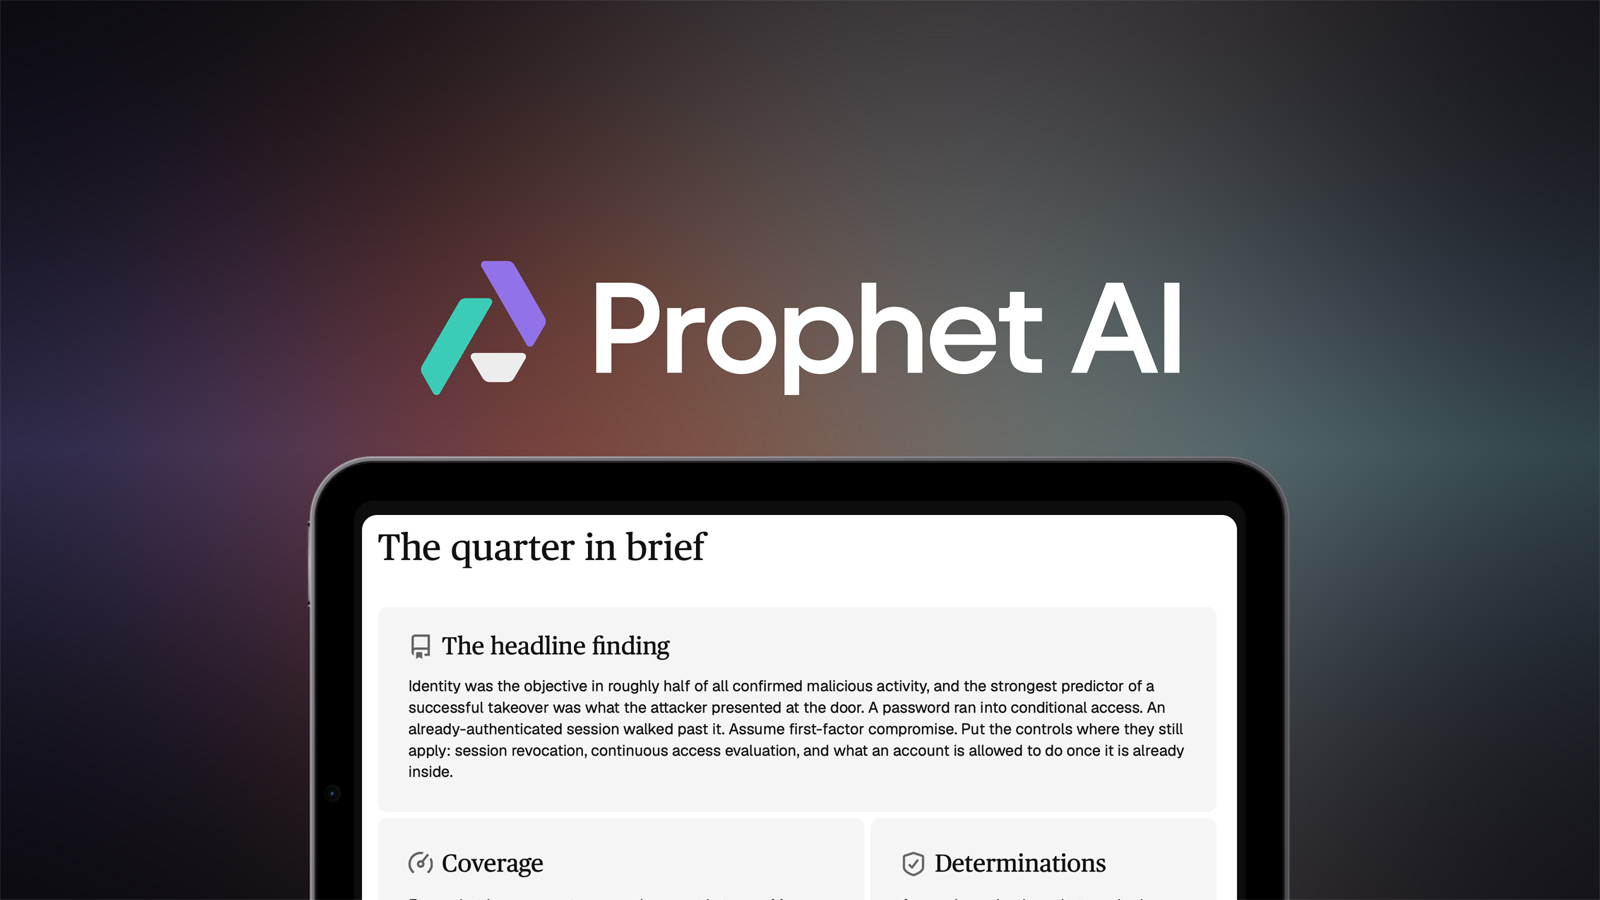
- Identity was the target in roughly 50% of confirmed malicious activity during May-July 2026.
- Prophet Security's quarterly analysis examined customer environments across an unspecified scope.
- Four main attack patterns were identified, though detailed descriptions were not provided in the initial report.
- Some attacks succeeded while others were blocked, but specific success rates were not disclosed.
Related Security News

Relays Mask Chinese Access to Frontier AI Models in the US
Dark Reading reports that over 80,000 AI relay servers are helping users in China mask their identities while accessing cutting-edge large language models (LLMs). The infrastructure is believed to facilitate unauthorized model access and potential cloning, though technical details remain unverified.

New PamStealer macOS Malware Variant Introduces Server-Side Decryption and Multi-Layer Persistence
Researchers from Jamf Threat Labs have identified a new variant of the PamStealer macOS malware that implements a server-side decryption chain for its main payload. The malware continues to rely on JavaScript for Automation (JXA) droppers but modifies lure and delivery methods. The decrypted payload enables live command-and-control communication and establishes multi-layer persistence on infected systems. No official patch is available; users are advised to avoid executing unknown scripts from untrusted sources.