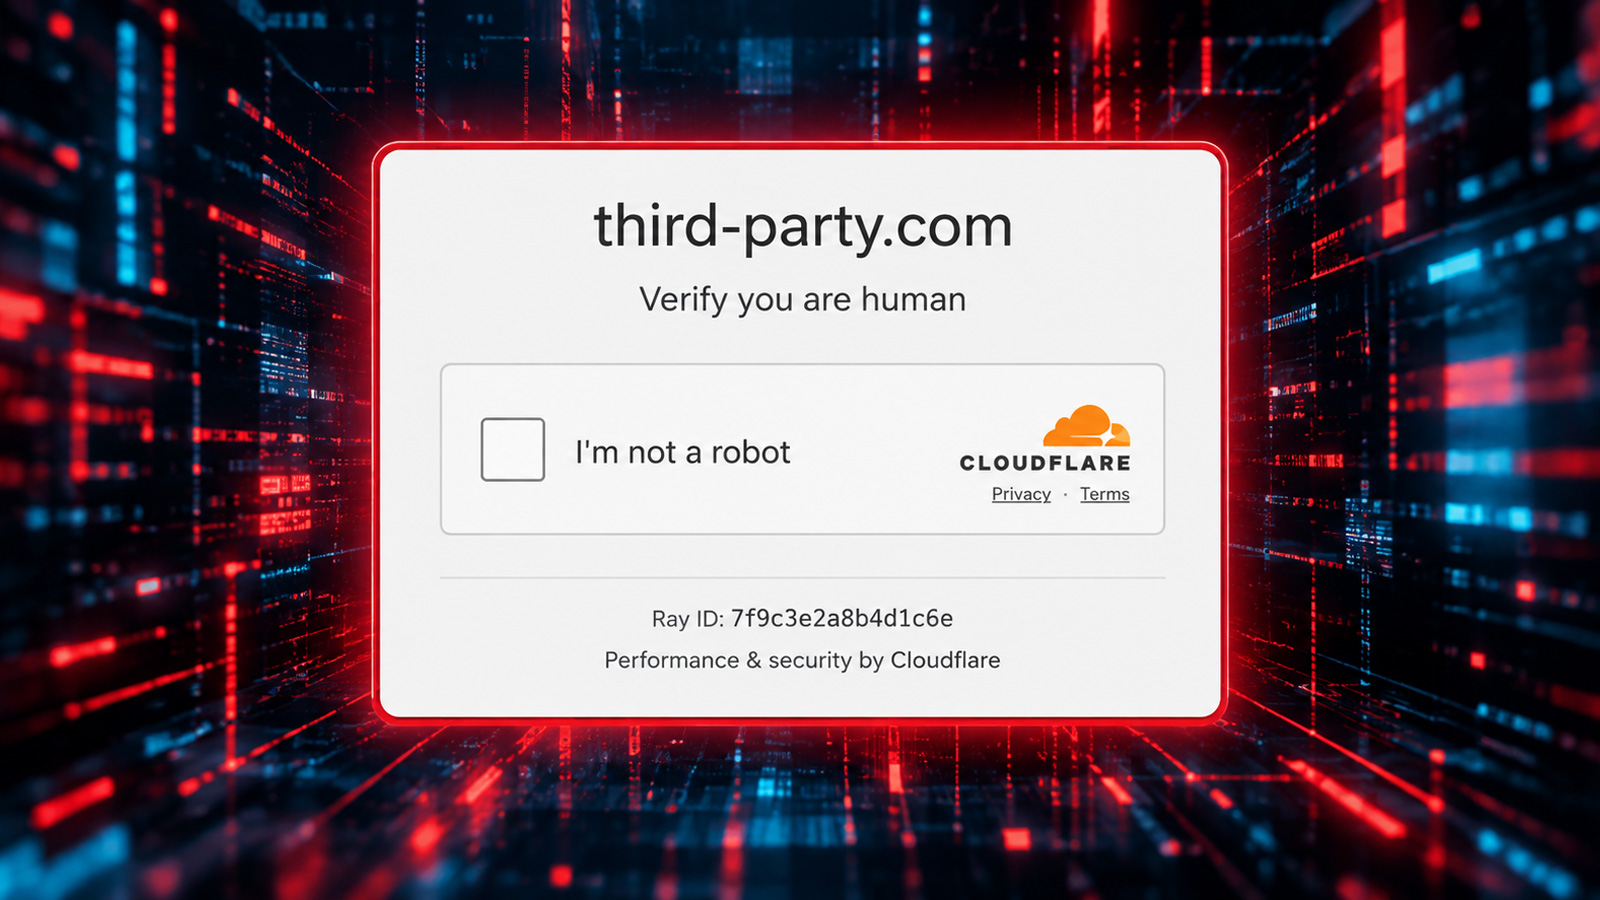
Placeholder Domain third-party.com Repurposed for ClickFix Attacks Targeting Windows Users
Fake Cloudflare verification pages serve PowerShell commands via developer documentation vectors
Key Takeaways
- The third-party.com domain, historically used as a placeholder in developer docs, has been compromised and is serving fake Cloudflare verification pages.
- Windows users are targeted via prompts to execute PowerShell commands, representing a ClickFix-style social engineering tactic.
- The attack exploits trust in Cloudflare branding and the familiarity of placeholder domains within code examples.
Related Security News

Former US Air Force Members Sentenced to Prison for Business Email Compromise Scams
Two former members of the United States Air Force were sentenced to a combined 189 months in federal prison for their roles in a multi-year series of business email compromise (BEC) scams and phishing campaigns. The sentencing, reported by BleepingComputer in September 2026, concluded a federal case targeting individuals who abused their military backgrounds to conduct financially motivated email fraud. The attacks spanned multiple years prior to sentencing, though specific victim counts and total financial losses were not detailed in the reporting. The case underscores the legal consequences of using military credentials and training for cyber-enabled fraud.



