Acronis Publishes Six-Point Ransomware Resilience Checklist for Managed Service Providers
Guidance focuses on reducing exposure, improving detection, preserving recovery points, and accelerating operational restoration across client environments.
Key Takeaways
- Acronis released a six-point ransomware resilience checklist for MSPs.
- The advisory covers reducing exposure, improving detection, preserving recovery points, and accelerating restoration.
- No specific active exploits or software vulnerabilities are addressed.
- Recommendations focus on attack surface reduction, detection improvements, and backup integrity.
- The guidance is advisory; full article required for complete details on the six capabilities.
Quick answers
- What happened?
- Acronis has released a six-point checklist designed to help managed service providers (MSPs) strengthen ransomware resilience. The advisory outlines capabilities spanning reduced exposure, attack detection, recovery point preservation, and rapid operational restoration. The guidance is advisory in nature and does not address a specific active exploit or vulnerability.
- What should defenders do?
- MSPs should review the checklist capabilities, reduce attack surface, enhance detection controls, verify backup integrity, and develop rapid restoration procedures.
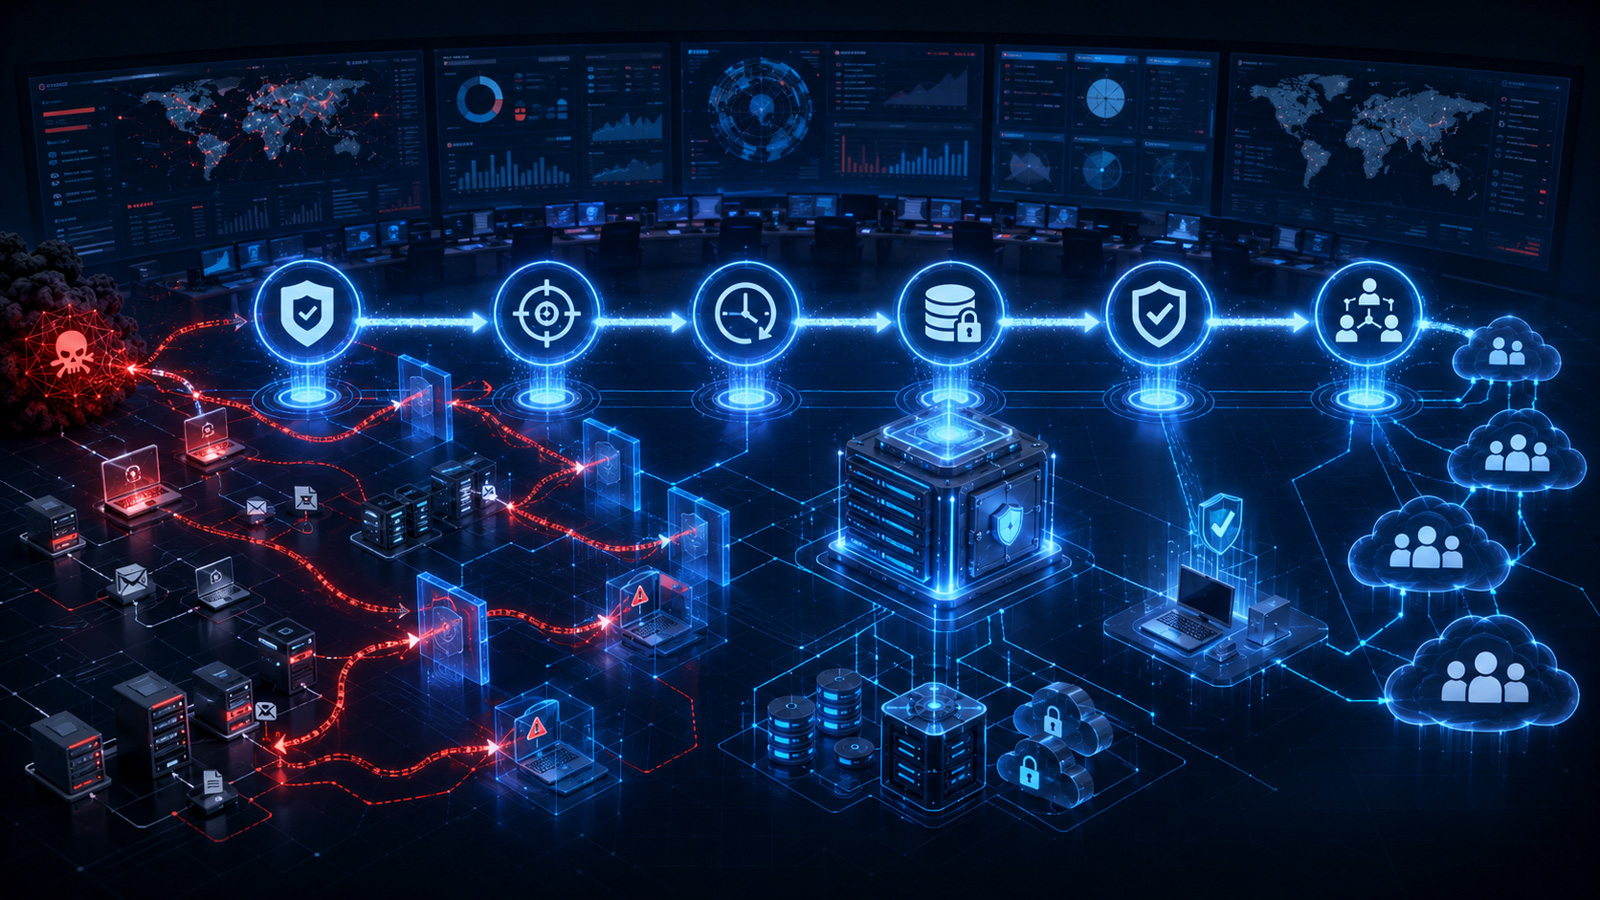
Acronis published a six-point checklist for managed service providers aimed at improving ransomware resilience and enabling faster recovery across client environments. The advisory emphasizes that ransomware protection requires more than backups or endpoint detection alone. The six capabilities outlined address reducing exposure, detecting attacks earlier, preserving recovery points, and restoring operations quickly following incidents. The guidance is intended for global MSP client environments and does not report specific exploitation details or require software patching. Instead, recommendations focus on reducing the attack surface, improving detection mechanisms, and ensuring backup integrity. The report was issued by BleepingComputer on 2026-09-02. As of the publication date, no confirmed active exploits or victim details associated with the checklist were reported.
Security Details
The advisory provides defensive guidance for MSPs to improve ransomware readiness. It does not describe a CVE, active exploit, or software vulnerability requiring a patch.
Mitigation
MSPs should review the checklist capabilities, reduce attack surface, enhance detection controls, verify backup integrity, and develop rapid restoration procedures.
Sources
BleepingComputer
Ransomware protection for MSPs: A 6-point checklist for faster recovery
Sep 2, 2026 · 14:02
Original link
Related Security News

Bitget Reports $388M Loss Following Exploitation of Third-Party Security Product Flaw
Bitget disclosed that an attacker stole approximately $388 million by exploiting a vulnerability in a third-party security product integrated into the exchange's infrastructure. The threat actor used the flaw to obtain high-level internal credentials, which were subsequently used on September 24 to issue fraudulent withdrawal commands to Bitget's wallet system. The exchange confirmed that most user funds remain secure, though the full extent of exposure is under investigation.




