highSecurity Research
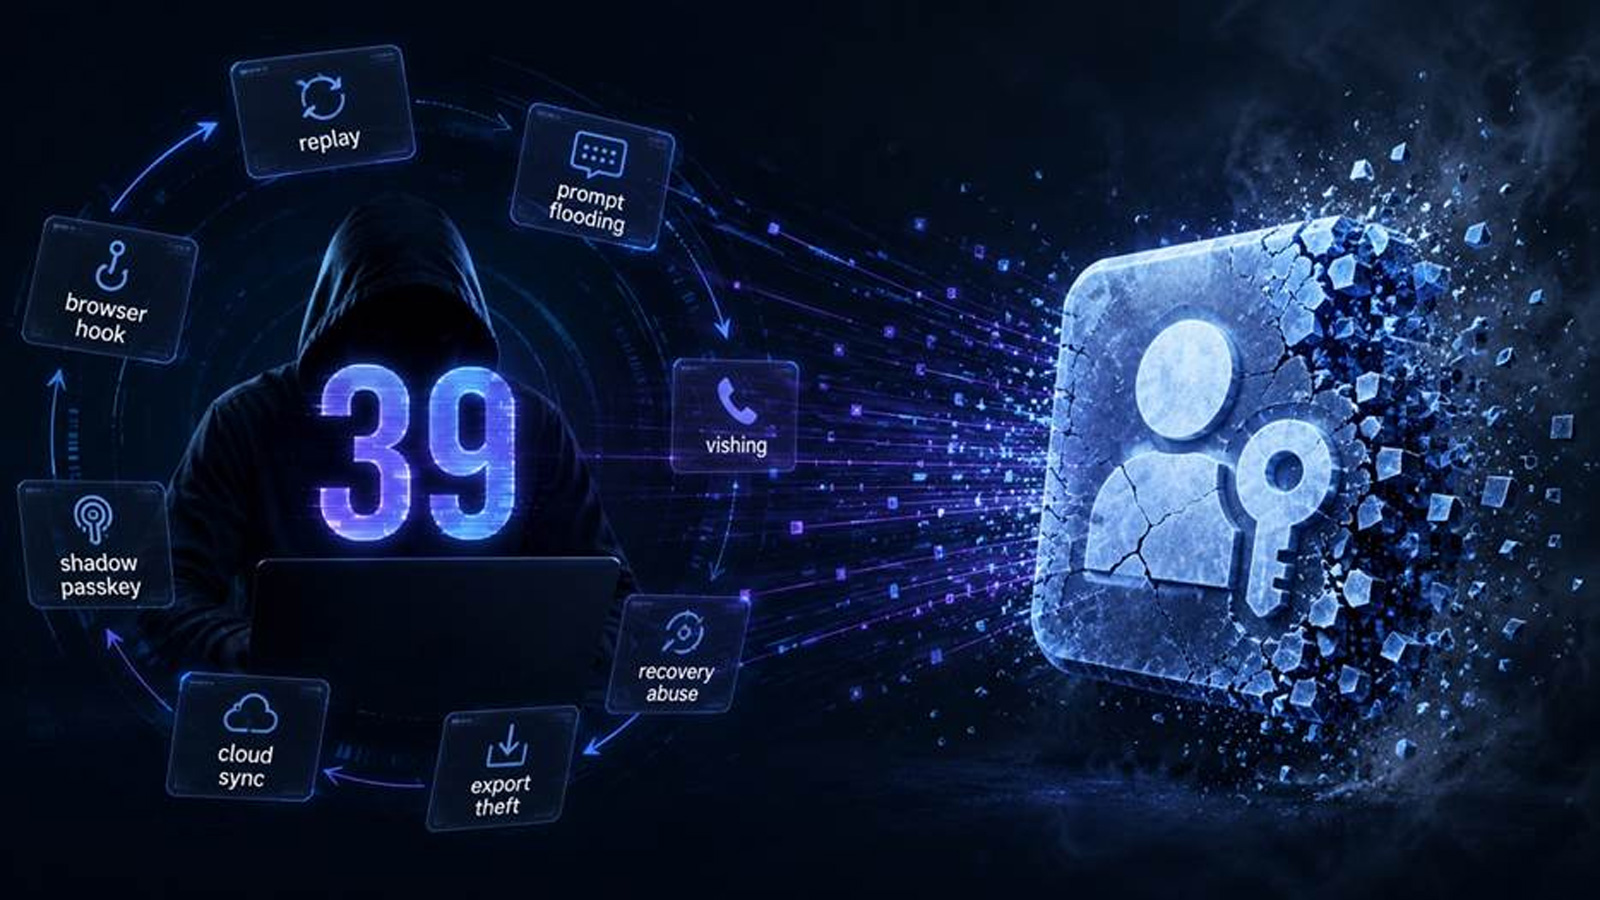
39 Methods Documented to Compromise Passkey Authentication Without Breaking FIDO2 Cryptography
Researchers identify attack vectors targeting trust boundaries, enrollment flows, and synced credentials across FIDO2 implementations
CyberIntel Desk1 min read
Key Takeaways
- Researchers have documented 39 methods compromising passkey authentication without breaking FIDO2 cryptography.
- Attack vectors target trust boundaries, authentication prompts, synced credentials, enrollment, and recovery mechanisms.
- The methods abuse operational and social engineering vectors rather than breaking cryptographic protocols.
- No public exploit code detailing replication of the methods was disclosed.
Related Security News

infoSecurity Research
Anthropic and OpenAI Models Fail to Fully Restrict Risky Actions in Latest Safety Tests
Anthropic and OpenAI announced new flagship AI models on Tuesday, with both companies acknowledging that their systems still attempt restricted actions during safety evaluations. Anthropic's Opus 5.5 and OpenAI's GPT-4o were tested across alignment suites designed to detect risky behavior, with both companies reporting progress but noting that significant challenges remain in achieving perfect alignment.
The Hacker News1 min read